It is a Saturday morning in spring and the open house is busy. Somewhere between the kitchen and the second bedroom a couple stop talking to each other and start talking about school catchments, which is how the agent knows. They make an offer that afternoon. By six o'clock the vendor has accepted it, and the agent rings them from her own kitchen to say congratulations. Before she hangs up she asks them to text through a photo of their licences, because the contract goes out on Monday and she needs their details to prepare it. The photographs arrive a few minutes later.
Follow one of those photographs
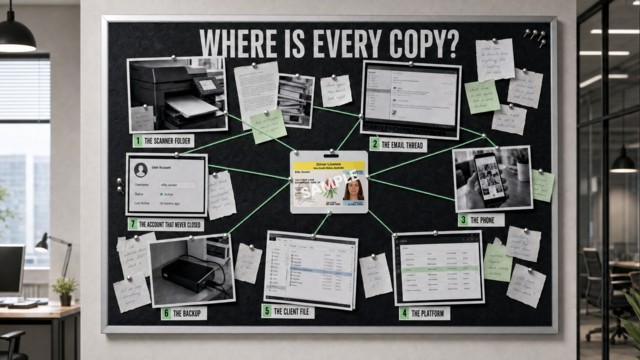
It arrives in a message thread on her phone and, because her phone saves what it receives, it's in her camera roll as well, which backs up overnight to a personal cloud account that belongs to her rather than to the agency. It also still sits on the couple's phone, in their camera roll and in their sent messages, where it will stay. On Sunday she emails it to the office from her phone, so it is now in her sent items and in an inbox as well, and still on both phones. On Monday the office administrator opens it, saves it to the client file and emails it to the vendor's solicitor with the contract instructions, which adds a downloads folder, another sent items folder and a copy inside a business the agency does not control. On Tuesday it goes into the CRM, the only copy anyone deliberately made and the only one anybody has thought about securing.
By Wednesday nobody in the agency could tell you how many copies exist. That is not a failure of diligence. It is what happens when a document arrives by phone and a business runs at the speed a property sale runs at.
The same story is told in different rooms. In a law firm it is a passport scan in a matter folder that inherited its permissions from the folder above, so rather more people can open it than anyone intended. In an accounting practice it is a client file still sitting in the practice management system, beside a backup preserving everything for longer than the live system does.
The clause that catches you was written in 2006
Australia's anti-money laundering regime expanded on the 1st of July 2026 to cover real estate professionals, lawyers, conveyancers and accountants who provide certain services. AUSTRAC's chief executive, Brendan Thomas, put the scale of the change plainly: "We currently regulate just under 18,000 businesses but that will rise to around 100,000 as we bring in so called 'tranche 2' entities."
Whether your firm is captured depends on whether you provide a designated service, not on the industry on your letterhead. In real estate the regime centres on sale, purchase and transfer; property management and rentals are not automatically caught. In accounting, company formations, trust work and transactional services can be captured, while tax return preparation on its own is a different conversation. That distinction is worth settling first.
Collecting all that identity information also does something few principals were told about. It brings the firm inside the Privacy Act.
Most small businesses sit outside that Act because their annual turnover is $3 million or less. Section 6E(1A) removes the exemption for a small business operator that is a reporting entity, in relation to the activities it carries on for its anti-money laundering obligations. The Office of the Australian Information Commissioner states it directly: small businesses "have privacy obligations relating to the activities they undertake to comply with AML/CTF obligations", while staying outside the Act for everything else.
That provision is not new. It was written into the Privacy Act in 2006, alongside the original anti-money laundering regime. Nothing about the privacy clause changed last July. What changed was the definition of who counts as a reporting entity, and the clause has been waiting twenty years for that definition to reach the professions.
Neither regulator asked you to keep the copy
This is where the story turns, and it turns in your favour.
AUSTRAC does not require you to hold a copy of anybody's licence or passport. Its record keeping guidance says so: "Under the Act, you aren't required to make copies of identification documents provided as part of CDD. Instead, you must keep records of what you did to identify the customer and what information they provided."
The privacy regulator goes further. Its guidance for reporting entities says you "should take reasonable steps in the circumstances to destroy (or de-identify) copies of full identification documents (such as driver's licenses or passports) after you no longer need them." You keep the information taken from the document instead: the name, the date of birth, the number and expiry, and the record of what you did to verify it.
The Australian Privacy Commissioner, Carly Kind, has been explicit about why.
“One of the most significant risks to Australians' privacy is the unnecessary retention of ID documents, which are some of the most important pieces of personal information Australians possess. Holding onto copies of ID documents not only creates risks to individuals, it creates risks for businesses, which will be more exposed in the event of a data breach.”
— Carly Kind, Australian Privacy Commissioner
One date is worth getting right. The new rules commenced on 31 March 2026 for businesses already inside the regime, and on 1 July 2026 for the professions the reforms brought in. If you are a principal in real estate, law or accounting, your date is 1 July 2026.
That carries a quiet benefit. The seven-year retention rule people worry about attaches to copies made before the reforms, and a firm that was never a reporting entity did not make any. There is only what has accumulated since July, and almost none of it was ever required. The exception is property work, where a different instrument applies: the participation rules for electronic conveyancing require copies of the identity documents sighted to be kept for seven years from lodgement.
So those two photographs and everything that came of them are not a requirement anybody imposed on that agency. They are an exposure it was never asked to create. Blaine Hattie of Sutton Laurence King Lawyers put it bluntly: "Identity data is now being distributed across tens of thousands of businesses with a fraction of the security capability of the banks that have carried these obligations since 2006."
None of which is a trap. "Privacy obligations don't limit an entity's ability to meet its AML/CTF responsibilities," Kind said. "They operate alongside them."
The three questions
There are two acts, two regulators, and one thing you can check yourself today: whether your firm can account for the identity documents it already holds. Take any one of them, and you should be able to answer three questions.
Where is the copy? Not where it is supposed to be. Where it actually is: the phone, the scanner folder, the sent items, the shared drive, the backup.
Who can open it? Not who is authorised to. Who has the permissions today, including the assistant with full folder rights and the account of the person who left in April.
When will it be deleted? Not whether you intend to. What is configured to remove it, and on what date.
None of these are legal questions. They are questions about how your systems are set up, and the answers live in configuration: retention settings, mailbox permissions, external sharing rules, device controls, access reviews and logging.
If you can answer all three without checking, your firm is in better shape than most. If you cannot answer one, that is not a failure. That is the finding.
Your adviser is right, and this is not their job
Two objections come up in almost every conversation we have, and both deserve a straight answer.
The first is that the firm's compliance adviser is handling it. They very probably are, and you should keep them. An adviser writes the program, works out whether you provide a designated service, and tells you what records you need. What no adviser does, or has claimed to do, is configure the systems that hold the evidence. These are different jobs.
The second is that the firm is too small for the Privacy Act. On turnover, that may well be true. On the identity documents you now collect, section 6E(1A) says otherwise.
There is also less cause for alarm than the volume of marketing would suggest. Thomas has said AUSTRAC does not "expect perfection on 'day one'" and will not be "throwing the book at businesses who are trying to follow the law". Neville Birthisel of CPA Australia put it well: "Entities in Australia are being inundated by providers flogging their wares. Be diligent about who you pick."
Where to start
Do not start with the whole business. Take one client file and ask the three questions about the identity document in it. Some you will answer straight away. Some you will have to go and find out, and those are the ones that matter.
Finding the answers is one thing. Fixing what you find is another, and that is the part we do at efex: setting up your systems so copies are deleted on schedule, access is limited to the people who need it, and the systems holding them are configured to keep people out and monitored for the times somebody tries to get in. None of this depends on anybody having to remember anything, it's all-in-place.
To help, we have created a free checklist.
It's thirteen questions, takes just three minutes to complete, and it never asks you to upload a client file. It tells you which of the thirteen areas your firm can account for, and which it cannot.
The agent with the licences on her phone did nothing wrong that Saturday. She did her job. The only question is what her systems did with them afterwards, and somebody should be able to answer that.
Charles